12
Key Facts
- Fast results Get in-depth threat context for any indicator quickly, with a 2-second response time, right after the registration and with no search requests limit for free. Simplify and speed up your investigation to quickly identify and prevent threats.
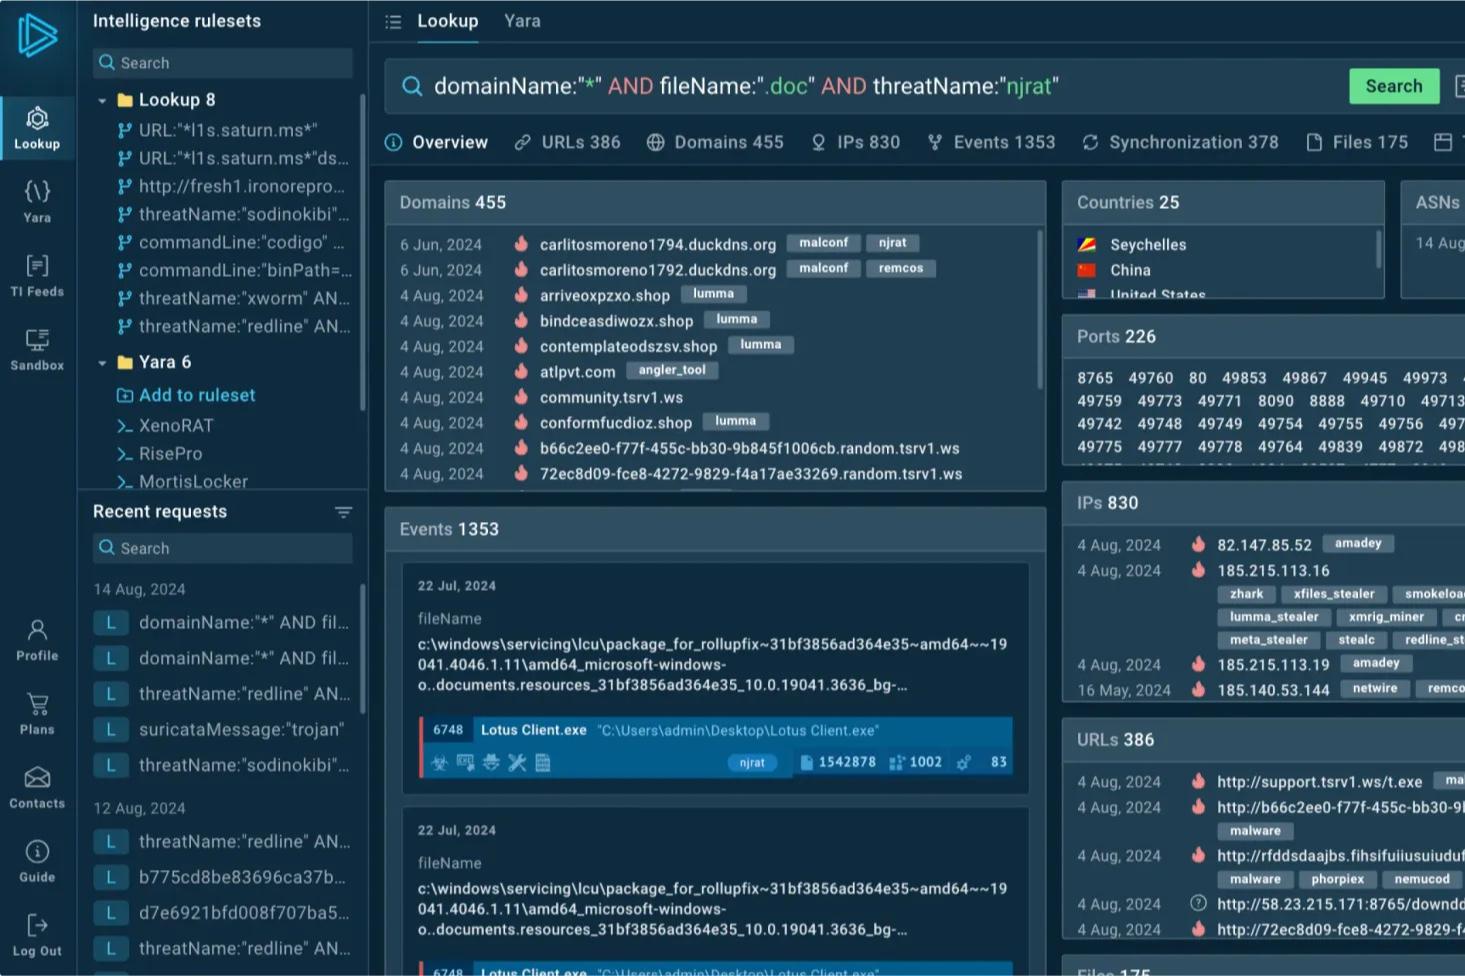
- Threat context enrichment Gather extensive information on any threat using a wide range of search parameters, including threat names, file hashes, IPs, registry keys, and YARA rules. Explore sandbox sessions where detected indicators were found to see how the entire attack unfolds.
- Attack data from 16,000 companies Leverage real-time, community-driven threat intelligence from samples uploaded by over 700,000 analysts worldwide to enhance proactive security and improve SOC efficiency. Discover unique data not found elsewhere.
Category
Threat analysis
Product information
ANY.RUN Threat Intelligence helps enterprise SOC teams and MSSPs strengthen threat detection, accelerate investigations, and improve incident response.
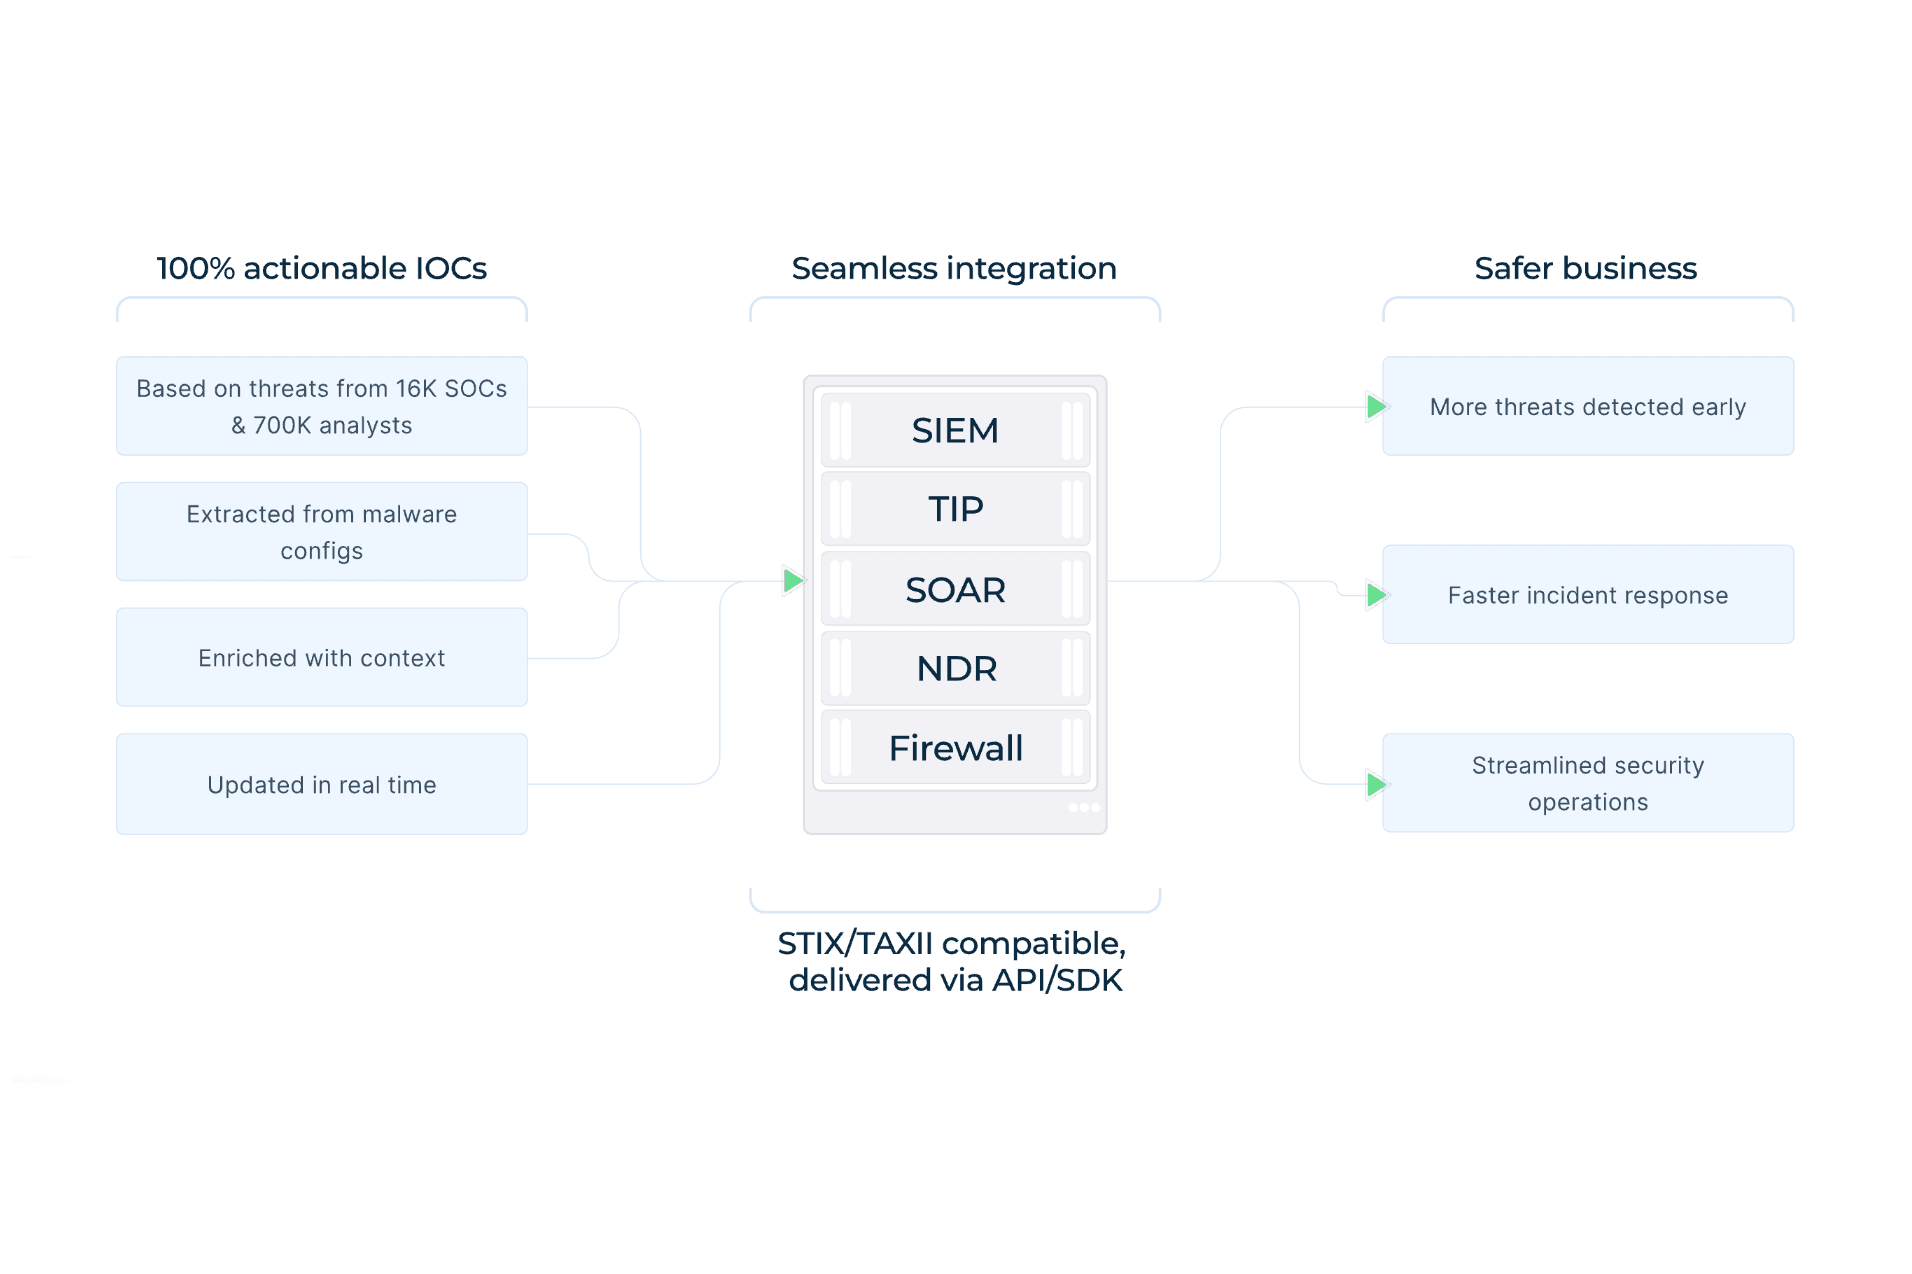
Built on real-world malware and phishing investigations from 16,000+ companies, it provides actionable threat intelligence through its four modules: TI Lookup, TI YARA Search, TI Feeds, and TI Reports. Security teams can validate and enrich indicators of compromise (IOCs), access behavioral context, identify emerging threats, and improve threat hunting. Through continuously updated threat data and integrations with SIEM, SOAR, and other security solutions, ANY.RUN TI