11
Key Facts
- All CRA obligations in one platform: from SBOM to EU declaration of conformity
- 24 h / 72 h reporting to ENISA and CSIRTs, CSAF advisories
- Hosted exclusively by European providers
Categories
Vulnerability and patch management Compliance / GRC (products and services) Application security Cyber-physical systems security Asset management / IT documentation
Product information
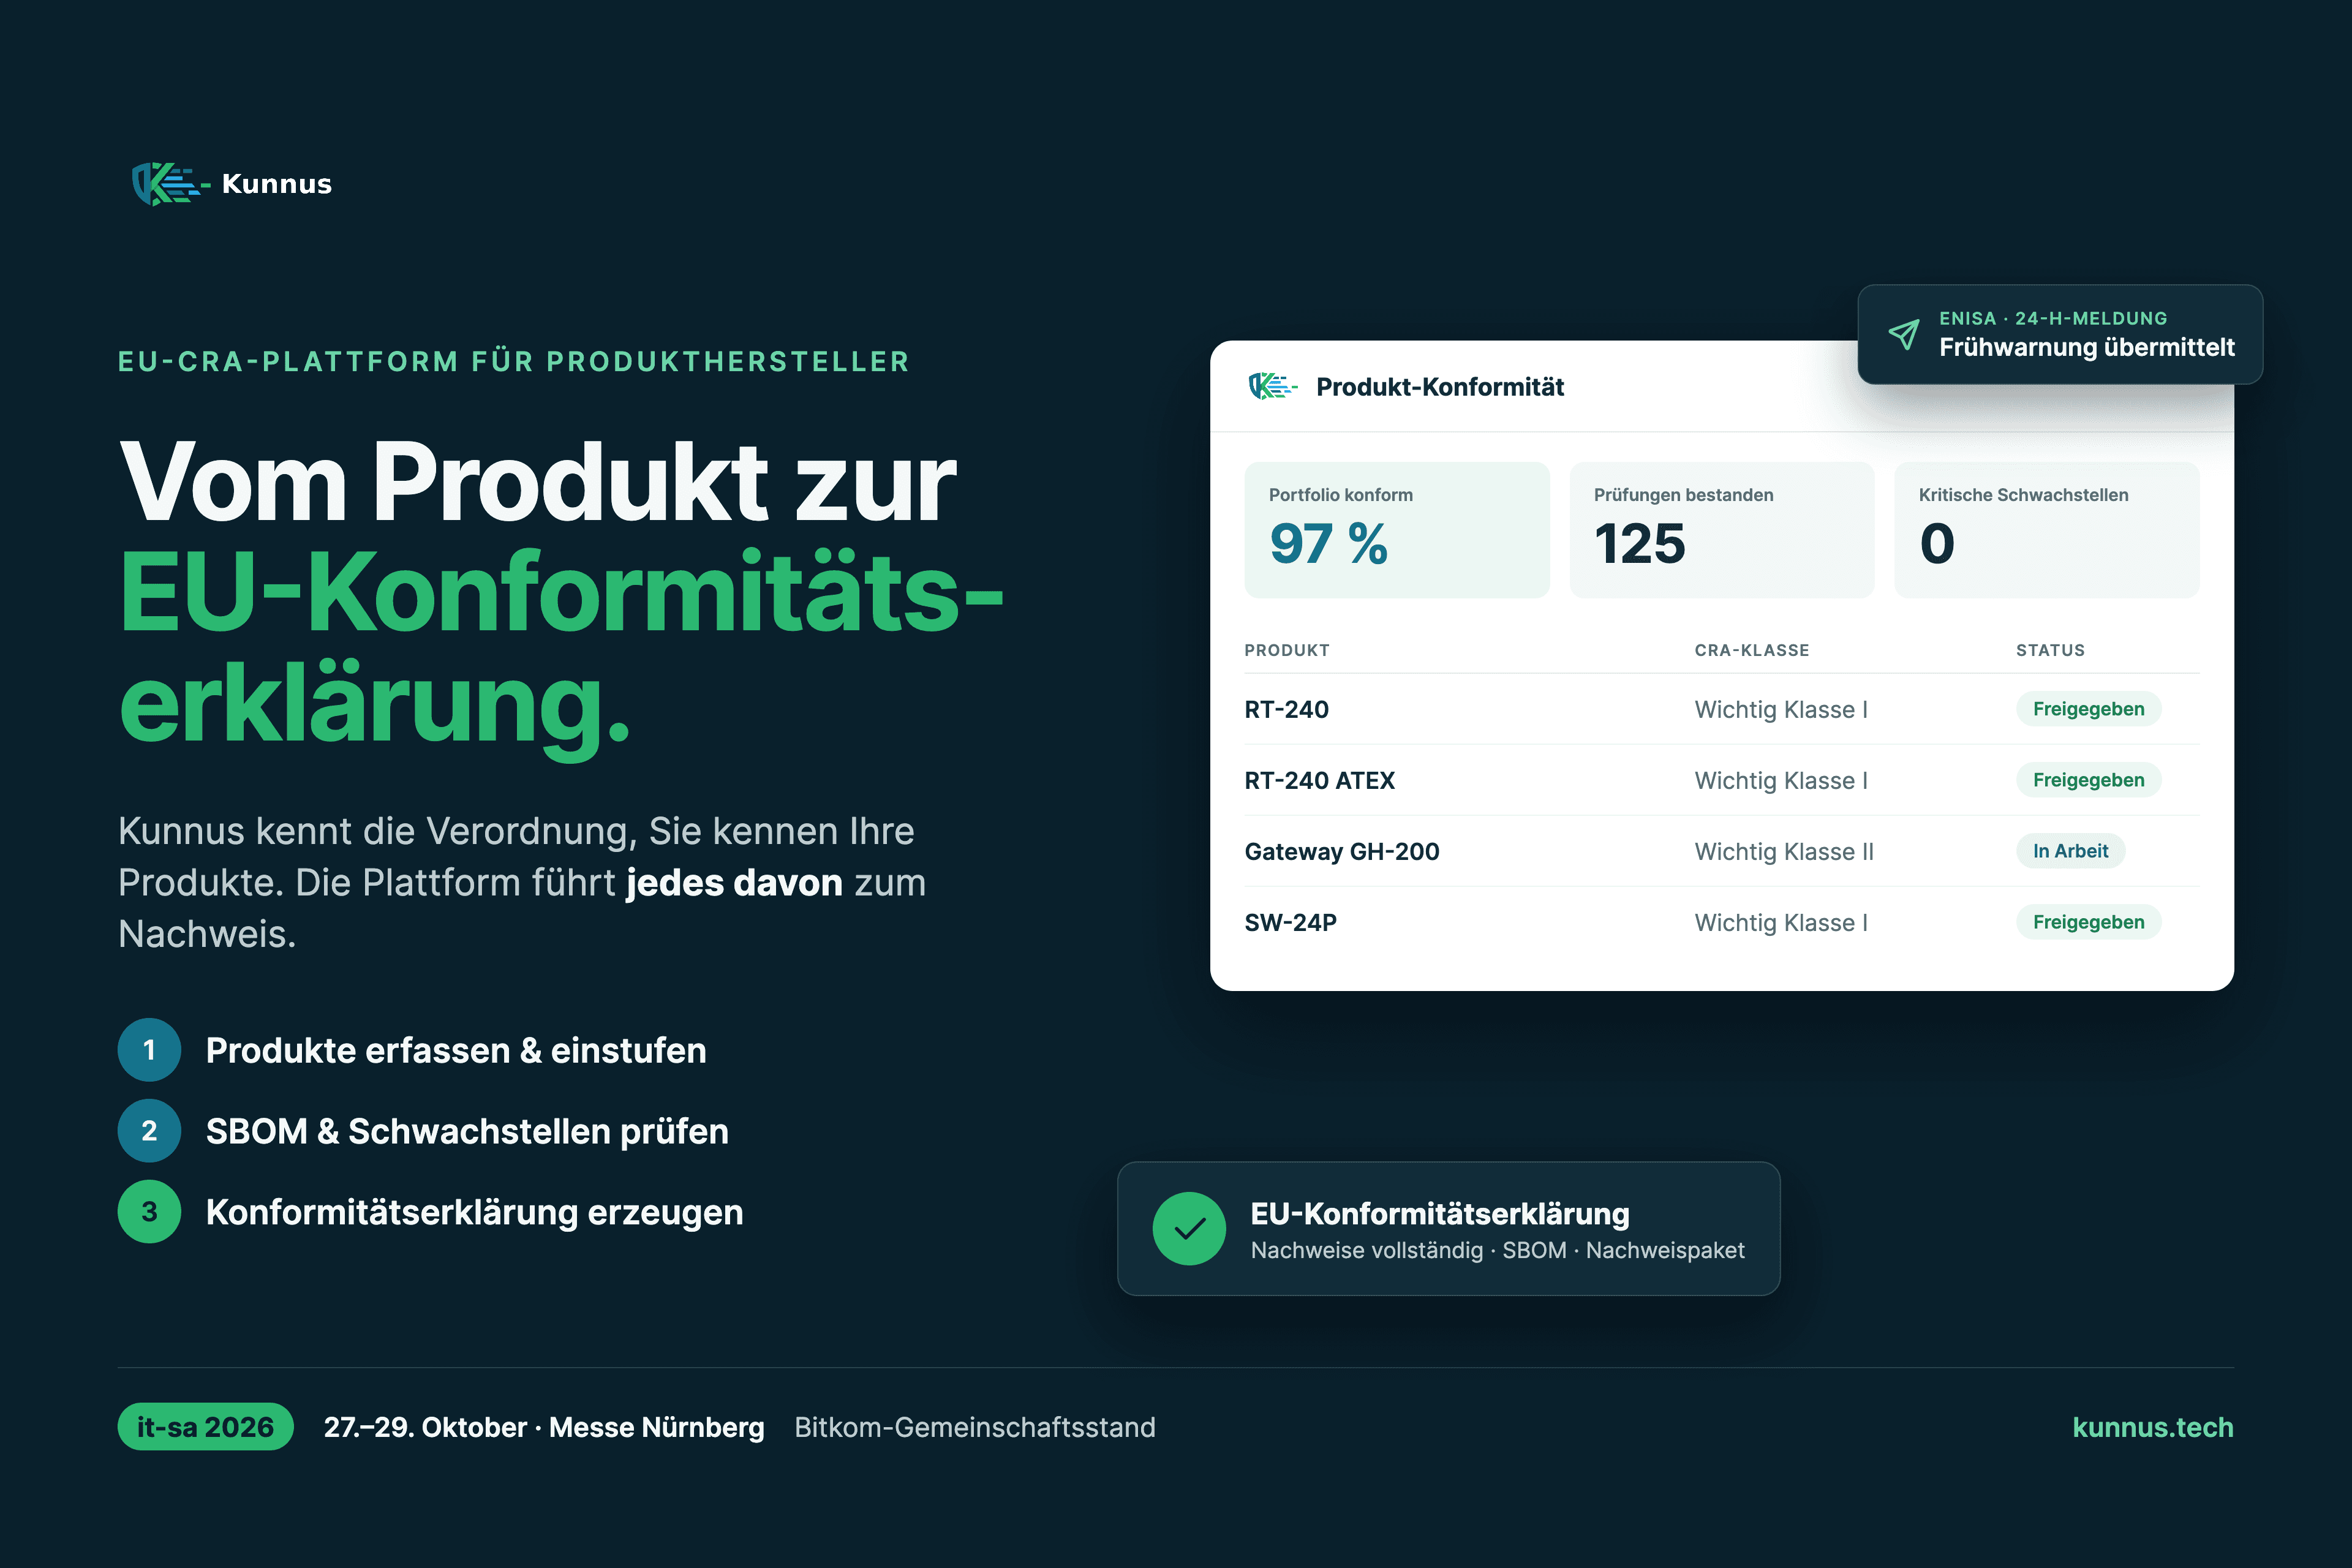
Kunnus maps the Cyber Resilience Act obligations for manufacturers into one platform. Products are inventoried and classified under the CRA (default, important class I/II, critical). SBOMs in CycloneDX and SPDX are checked continuously against NVD and OSV. For actively exploited vulnerabilities, Kunnus supports the 24 hour early warning and 72 hour notification to ENISA and CSIRTs and the publication of CSAF advisories. Annex I risk assessment, a supplier portal, technical documentation, conformity assessment (module A, B+C or H) and the EU declaration of conformity follow in the same system, with audit-proof evidence.
Product Expert