The password was changed. Is the attacker gone?
Infostealers steal live sessions, not just passwords. Why a password reset rarely ends the incident, and what closes the door.
Topic
When & Where
Details
Format:
Management lecture
Language:
English
Session description
Speaker: Sergiy Lapin
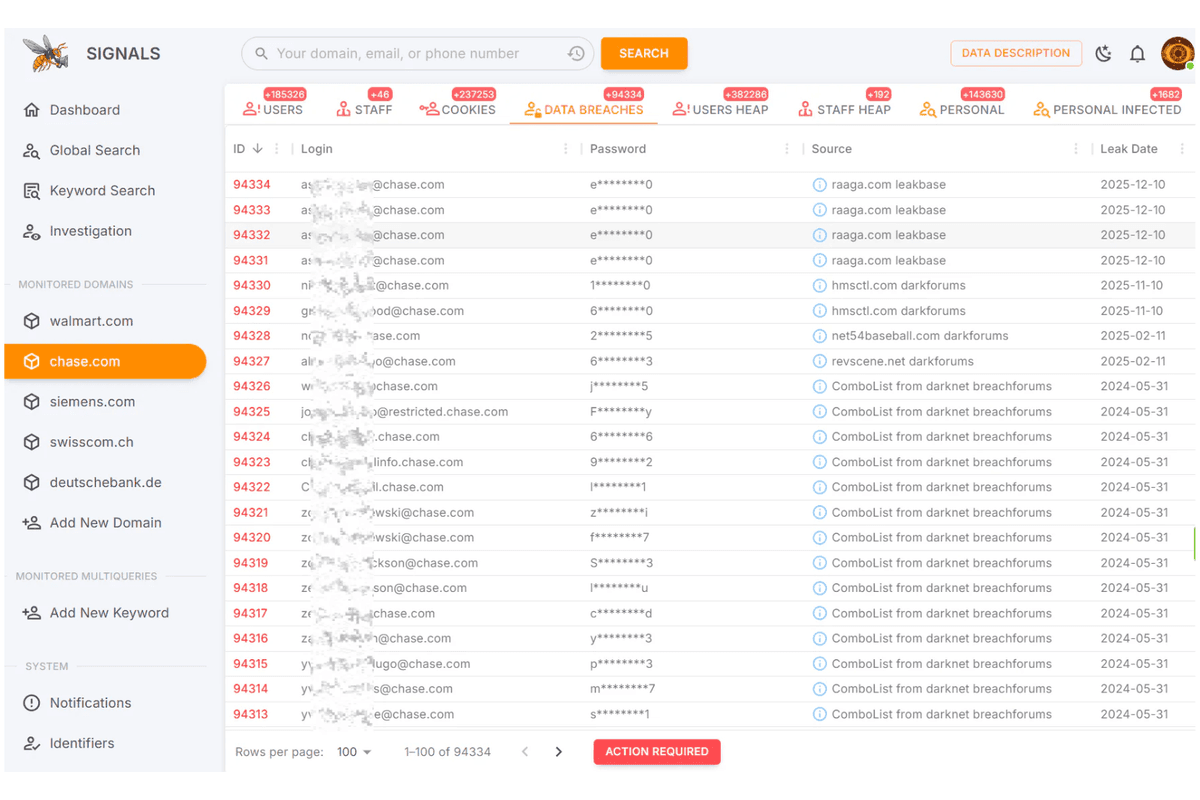
An infostealer does not steal a password. It steals a snapshot of someone's working life: saved passwords, live session cookies and tokens, API keys and enough device detail to impersonate the user. In August 2026, a single free stealer-log dump contained thousands of session tokens for Google, Microsoft and AI tools that had not yet expired. Increasingly, the infected machine belongs to a contractor or sits on a developer's personal desk – a device the security team has never seen.
This management lecture follows one stolen browser from infection to corporate SaaS data, based on current public research and incident reports from 2025 and 2026. It shows where the chain can be broken – and why the most common response, "we reset the pa ...