
11
idgard - Sealed Cloud
Key Facts
- Technical trust instead of contractual trust: Traditional cloud agreements (DPAs, SLAs, certifications) prohibit operators from accessing data. Sealed Cloud makes such access technically impossible. This can be demonstrated to auditors, regulators, and customers as an architectural proof, rather than relying solely on contractual assurances.
- Protection against extraterritorial access: A fully German and European legal chain consisting of company headquarters, data centers, personnel, and contractual relationships reduces exposure to the US CLOUD Act and similar non-European access claims.
- Flexible deployment models: Whether as a ready-to-use application (Sealed SaaS, such as idgard), a dedicated Private Cloud as a Service offering, sovereign managed cloud hosting, an on-premises deployment within your own data center, or a compact edge instance, the architectural principle adapts to your operating model.
Categories
Cloud (computing) security
Product information
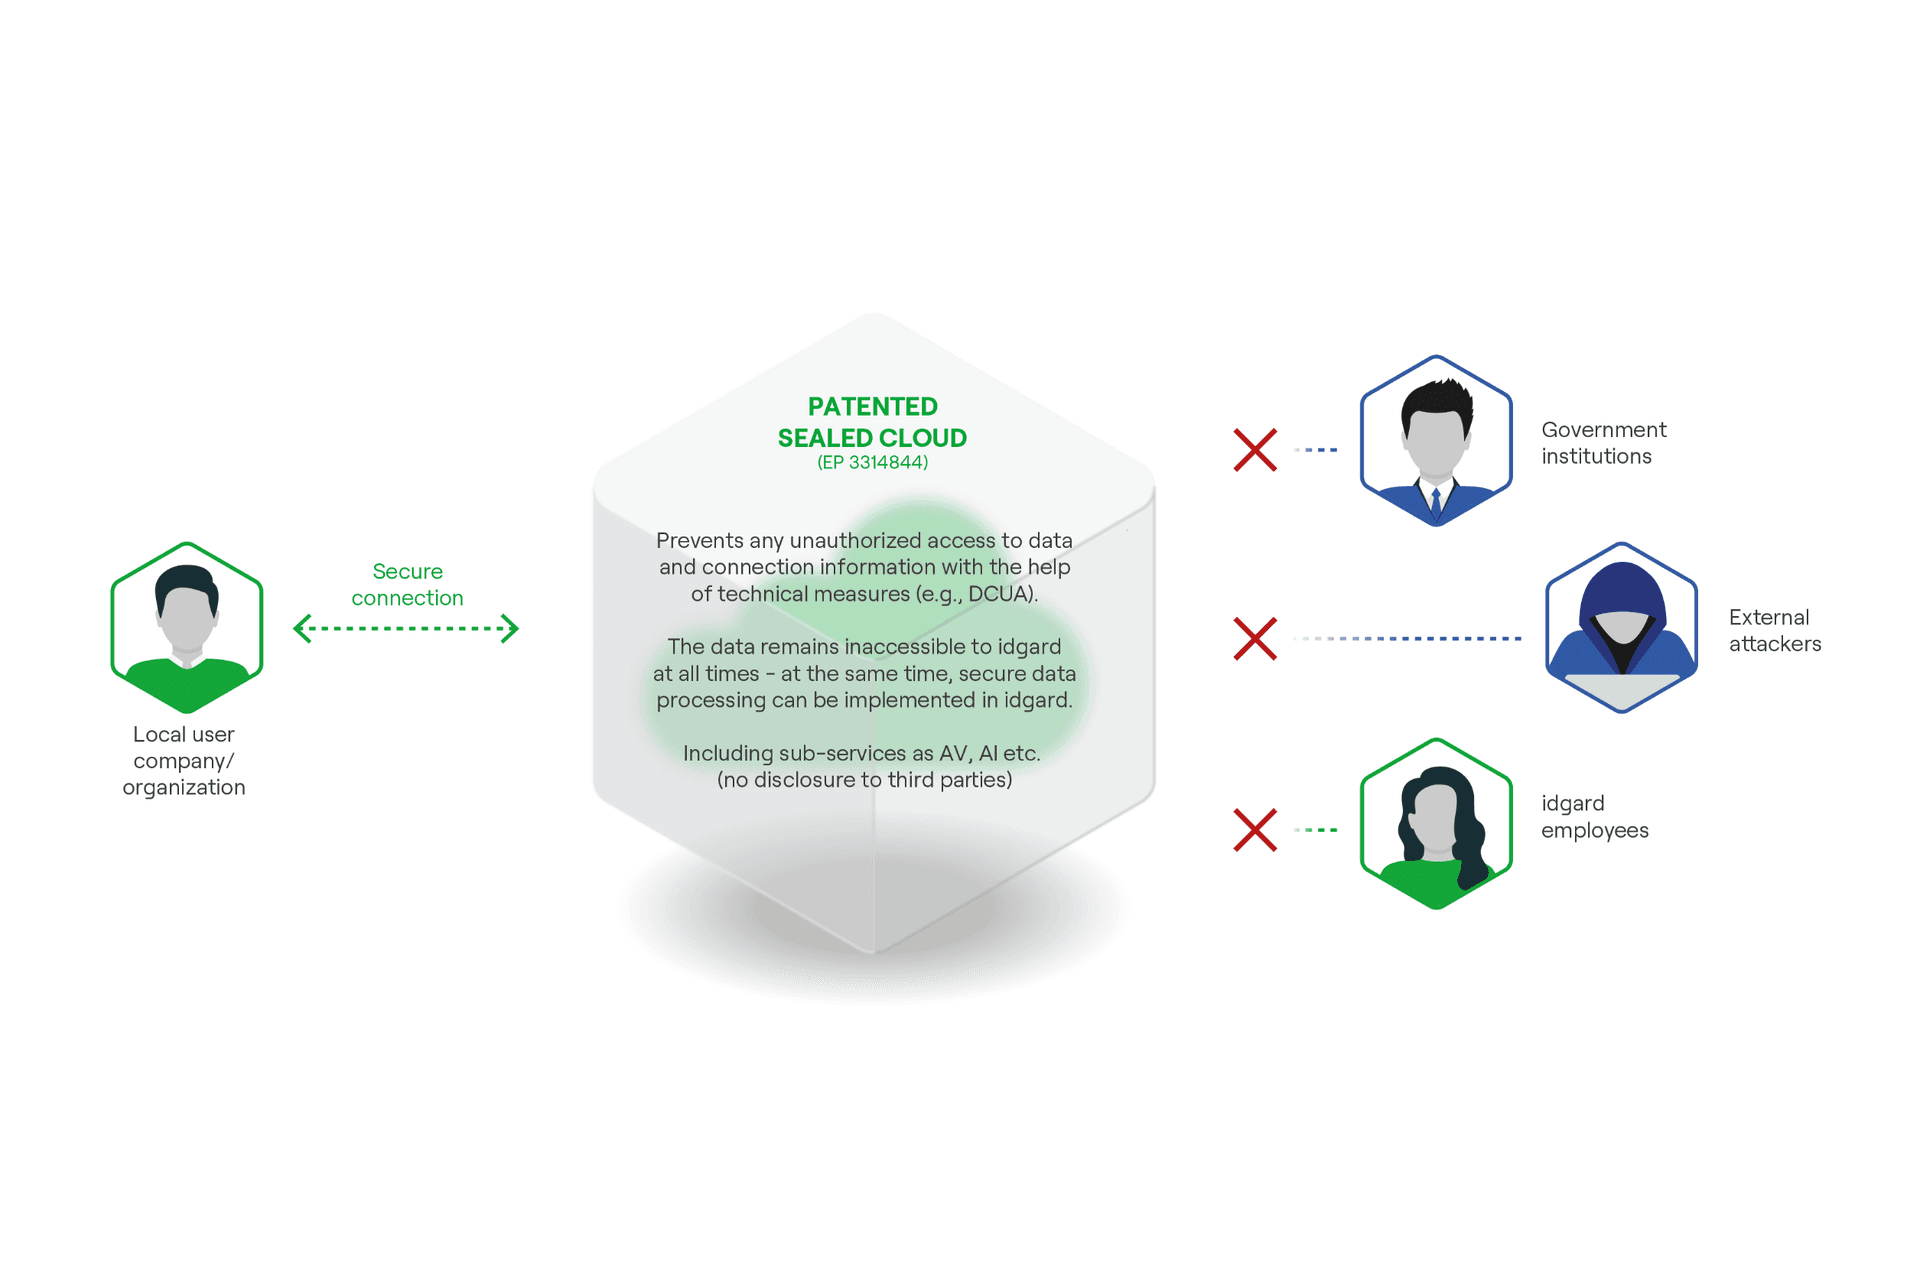
Cloud data is well protected today - as long as it is at rest or in transit. However, as soon as it is being processed, it resides unencrypted in RAM - accessible to anyone with sufficient administrative privileges, whether at the cloud provider, an insider, or through government access.
Sealed Cloud closes precisely this gap.Sealed Cloud is the technical architecture behind DriveLock idgard: It technically prevents the operator itself from accessing customer data - not just contractually, but through a combination of physical isolation, cryptographic protection, and automated control processes.
Product Expert
Christoph Dengler
Director PreSales Sales
Download product information